
Excessive access
Broad permissions increase the impact of compromised accounts.
Practical assessment and hardening for applications, cloud systems, data, and teams.
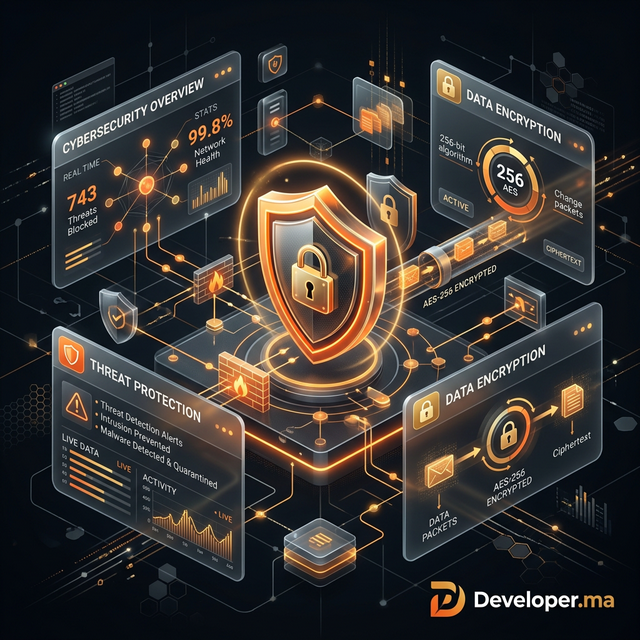
We assess agreed applications and infrastructure for weaknesses in access, configuration, and data handling. Findings are ranked by practical impact and followed by remediation guidance and scoped retesting.
Broad permissions increase the impact of compromised accounts.
Public services, leaked secrets, or unsafe defaults create unnecessary entry points.
Closing a ticket does not establish that a weakness has been removed.
We agree assets, permitted testing methods, and operational limits.
Reviews examine authentication, access controls, configuration, and exposed dependencies.
Findings include evidence, impact, and practical steps for the responsible team.
We recheck agreed corrections and document remaining exposure.
Severity and business context help teams address material issues first.
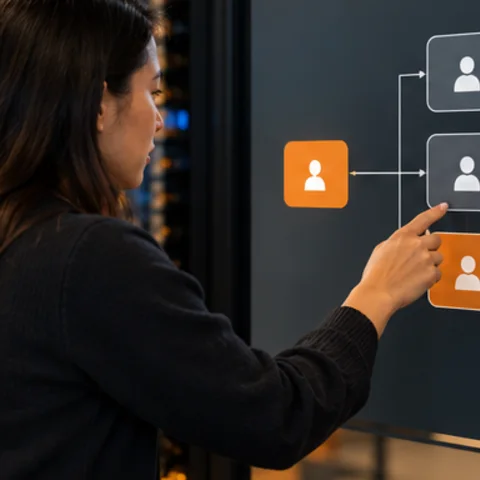
Least-privilege changes limit unnecessary reach across systems.
Retesting provides evidence that specific weaknesses were corrected.
Identify the applications or infrastructure you want assessed and any operational restrictions.
Clear answers to practical questions before starting.


 English
 phone
 Whatsapp
 Contact